HIPAA Compliance in Medical Billing
Medical billing is more than submitting claims and collecting payments. Every day, billing teams handle patient information that must stay private and secure. That is where HIPAA Compliance in Medical Billing becomes essential.
Whether you run a small private practice or manage a large healthcare organization, understanding HIPAA helps protect your patients, your reputation, and your revenue. A single mistake can lead to financial penalties, damaged trust, and unnecessary stress. The good news is that staying compliant is not as complicated as many people think. With the right processes, staff training, and security measures, you can confidently protect sensitive information while keeping your billing workflow efficient. This guide explains HIPAA in plain language, shares practical advice based on real billing situations, and provides useful checklists that you can start using today.
What Is HIPAA?
HIPAA stands for the Health Insurance Portability and Accountability Act. It is a federal law that protects patient health information and sets standards for how healthcare providers, insurance companies, clearinghouses, and medical billing companies collect, store, share, and protect sensitive data.
For medical billing teams, HIPAA is part of everyday work because patient information moves through multiple systems before a claim reaches an insurance company.
Why HIPAA Compliance Matters in Medical Billing
Medical billing professionals handle patient names, insurance details, medical diagnoses, treatment information, and payment records every day. All of this information is considered protected health information.
When that information is not handled properly, several problems can occur.
| Benefit of HIPAA Compliance | Why It Matters |
|---|---|
| Protects patient privacy | Builds trust with patients |
| Reduces legal risk | Avoids expensive penalties |
| Improves business reputation | Encourages provider confidence |
| Prevents data breaches | Protects sensitive records |
| Supports smooth claim processing | Reduces workflow interruptions |
Practices that invest in compliance often experience fewer security issues and stronger relationships with both patients and insurance companies.
What Is Protected Health Information
Protected Health Information, often called PHI, includes any information that can identify a patient.
Examples include:
| Protected Information | Example |
|---|---|
| Patient name | John Smith |
| Address | Home mailing address |
| Phone number | Mobile or office number |
| Medical record number | Patient ID |
| Insurance policy number | Health plan details |
| Date of birth | Personal identification |
| Diagnosis | Diabetes or hypertension |
| Lab reports | Blood work results |
| Billing information | Payment history |
Even a small piece of patient information can become protected when combined with medical details.
Who Must Follow HIPAA Rules?
Many people assume only doctors need HIPAA compliance, but the law covers far more organizations.
These include:
| Organization | HIPAA Applies |
|---|---|
| Physician offices | Yes |
| Hospitals | Yes |
| Medical billing companies | Yes |
| Insurance companies | Yes |
| Medical clearinghouses | Yes |
| Third party billing vendors | Yes |
| Healthcare software providers working with PHI | Yes |
If your business handles patient information in any way, HIPAA likely applies.
The HIPAA Rules Every Billing Team Should Know
Privacy Rule
The Privacy Rule controls who can access patient information and when it may be shared.
Medical billers should only access records needed to perform their job.
Example
A billing specialist reviewing diagnosis codes for claim submission is allowed access.
Looking through patient records out of curiosity is not allowed.
Security Rule
The Security Rule focuses on electronic patient information.
Organizations should protect digital records through security measures such as:
-
- Strong passwords
-
- Multi factor authentication
-
- Secure servers
-
- Data encryption
-
- Regular software updates
-
- Employee training
Breach Notification Rule
If patient information is exposed without authorization, organizations may need to notify affected patients and government authorities within required timeframes.
Quick action often reduces further damage.
Common HIPAA Violations in Medical Billing
Many violations happen because of simple mistakes rather than intentional misconduct.
| Common Mistake | Risk |
|---|---|
| Sharing passwords | Unauthorized access |
| Sending claims to the wrong email | Privacy breach |
| Leaving patient files unattended | Information exposure |
| Weak passwords | Increased hacking risk |
| Using personal devices without security | Data theft |
| Discussing patient details publicly | Privacy violation |
Most of these mistakes are preventable with regular staff education.
Practical Ways to Stay HIPAA Compliant
Train Employees Regularly
One training session during hiring is not enough.
Experienced billing managers often schedule refresher sessions several times each year because regulations, technology, and cyber threats continue to change.
Limit Access
Not every employee needs access to every patient record.
Use role based permissions so employees only see information required for their responsibilities.
Use Secure Software
Choose billing software that supports:
| Security Feature | Importance |
|---|---|
| Data encryption | Very High |
| User access controls | Very High |
| Audit logs | High |
| Automatic backups | High |
| Multi factor authentication | Very High |
Investing in secure software often costs much less than recovering from a data breach.
Create Strong Password Policies
Encourage employees to:
-
- Use unique passwords
-
- Change passwords regularly
-
- Never share login credentials
-
- Enable multi factor authentication
Simple habits dramatically reduce security risks.
Monitor System Activity
Regular audits help identify unusual account activity before it becomes a larger issue.
Many successful billing companies review access logs every month.
Real World Example
Imagine a billing employee accidentally emails a patient statement to the wrong person.
Without proper reporting procedures, the mistake could become a serious compliance issue.
A well prepared practice would:
-
- Report the incident immediately.
-
- Investigate what happened.
-
- Determine what information was exposed.
-
- Notify affected individuals if required.
-
- Update procedures to prevent future mistakes.
The goal is not simply avoiding penalties but reducing future risk.
HIPAA Compliance Checklist
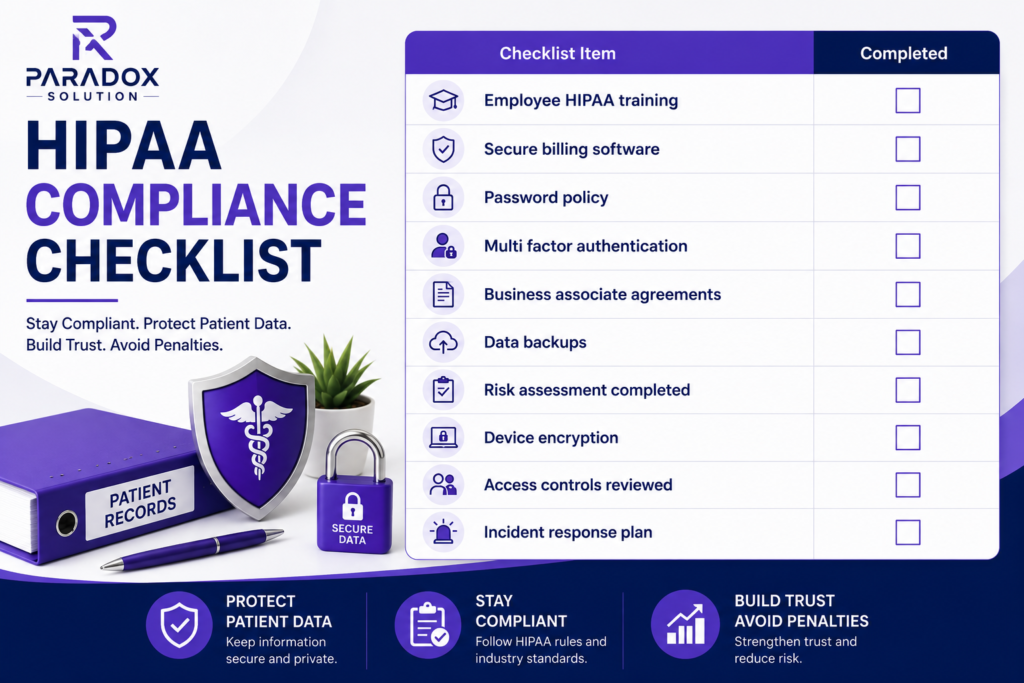
Review this checklist at least once every year.
Business Associate Agreements Matter
Many practices outsource billing to outside companies.
Whenever another company handles patient information, a Business Associate Agreement should be in place.
This agreement explains:
-
- Responsibilities
-
- Security expectations
-
- Privacy requirements
-
- Reporting responsibilities
Never work with a billing vendor that refuses to sign one.
How HIPAA Improves Patient Trust
Patients rarely ask about compliance until something goes wrong.
Practices that clearly demonstrate strong privacy practices often gain greater confidence from patients.
Benefits include:
| Advantage | Result |
|---|---|
| Better patient confidence | Higher satisfaction |
| Fewer complaints | Stronger reputation |
| Improved workflow | Better staff accountability |
| Better security | Lower business risk |
Trust remains one of the most valuable assets any healthcare practice can build.
Cost of Poor HIPAA Compliance
Ignoring HIPAA can become very expensive.
Potential costs include:
| Expense | Possible Impact |
|---|---|
| Government penalties | Significant financial loss |
| Legal fees | Expensive litigation |
| Lost patients | Reduced revenue |
| Reputation damage | Long term business impact |
| Data recovery | High technology costs |
| Staff retraining | Additional operational expense |
Prevention is almost always less expensive than recovery.
Best Practices for Medical Billing Teams
Review policies every year
Healthcare technology changes quickly. Policies should evolve with it.
Perform regular risk assessments
Finding weaknesses early saves time and money.
Encrypt sensitive information
Encryption protects data during storage and transmission.
Back up important files
Reliable backups reduce downtime after technical failures.
Work with trusted vendors
Choose vendors that understand healthcare privacy requirements.
Document everything
Good documentation demonstrates compliance efforts during audits.
Signs Your Billing Process Needs Improvement
Watch for these warning signs.
| Warning Sign | Recommendation |
|---|---|
| Shared employee accounts | Create individual logins |
| No security training | Schedule regular education |
| Outdated software | Upgrade systems |
| Missing audit logs | Enable activity tracking |
| No documented policies | Create written procedures |
| Weak password practices | Strengthen security standards |
Fixing small problems early prevents larger compliance issues later.
Final Thoughts
HIPAA Compliance in Medical Billing is not simply about following government regulations. It is about protecting patients, strengthening your practice, and reducing unnecessary business risk. Every claim, patient record, and insurance transaction carries sensitive information that deserves careful handling.
The most successful medical practices treat HIPAA as part of their daily culture instead of a yearly task. Regular staff education, secure technology, clear policies, and continuous monitoring all work together to create a safer billing environment.
Small improvements made consistently often provide the biggest long term benefits. By making privacy and security part of every billing process, your practice can build patient trust while avoiding costly mistakes and supporting sustainable growth.